Reports
One scan, three formats
Give stakeholders a readable PDF, and give your tools SARIF or JSON. These samples were made with FlawStrike's real exporters, using demo data for a fictional site.
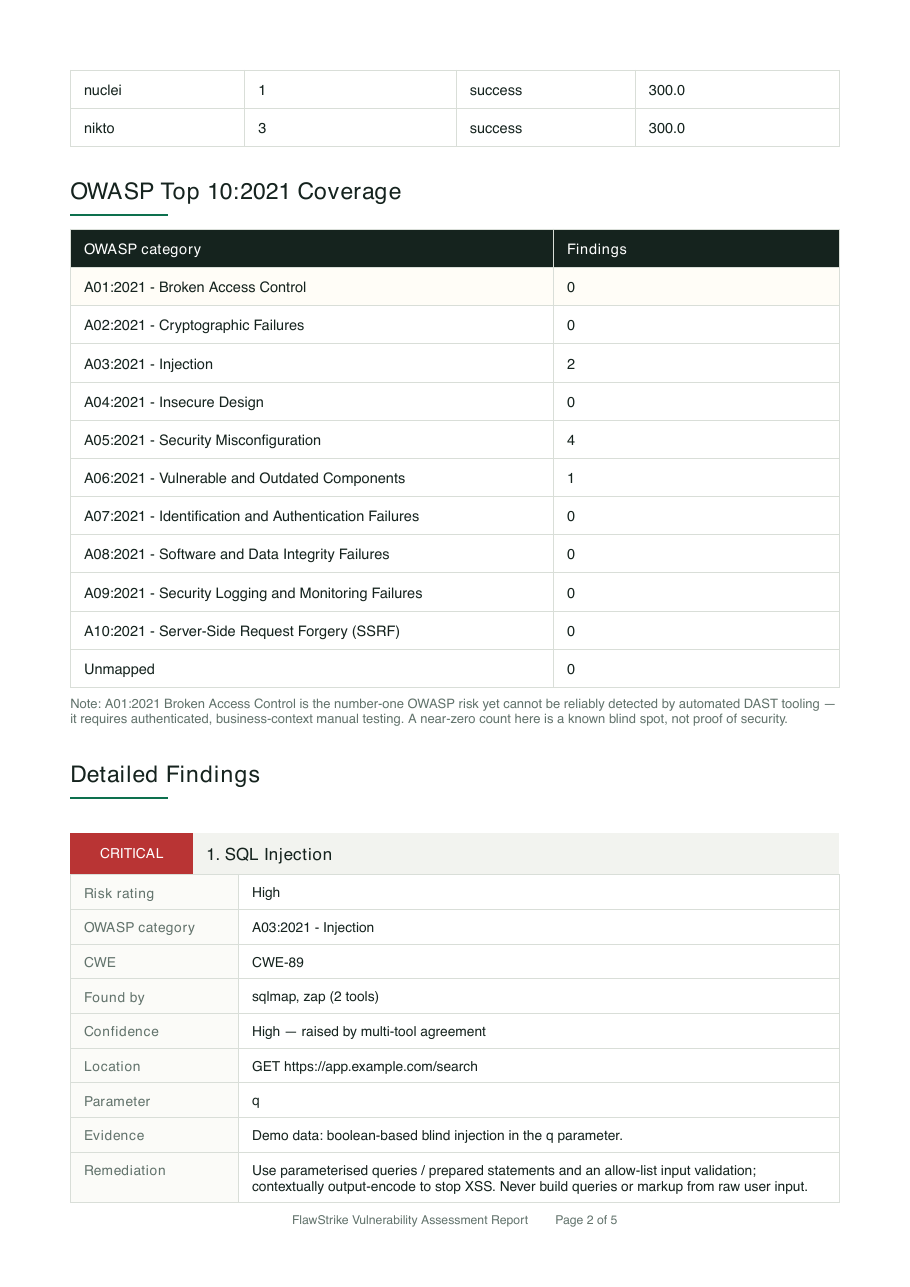
A report you can hand to anyone
An executive summary, engine and OWASP coverage, then each finding with its severity, location and evidence.
Download sample PDF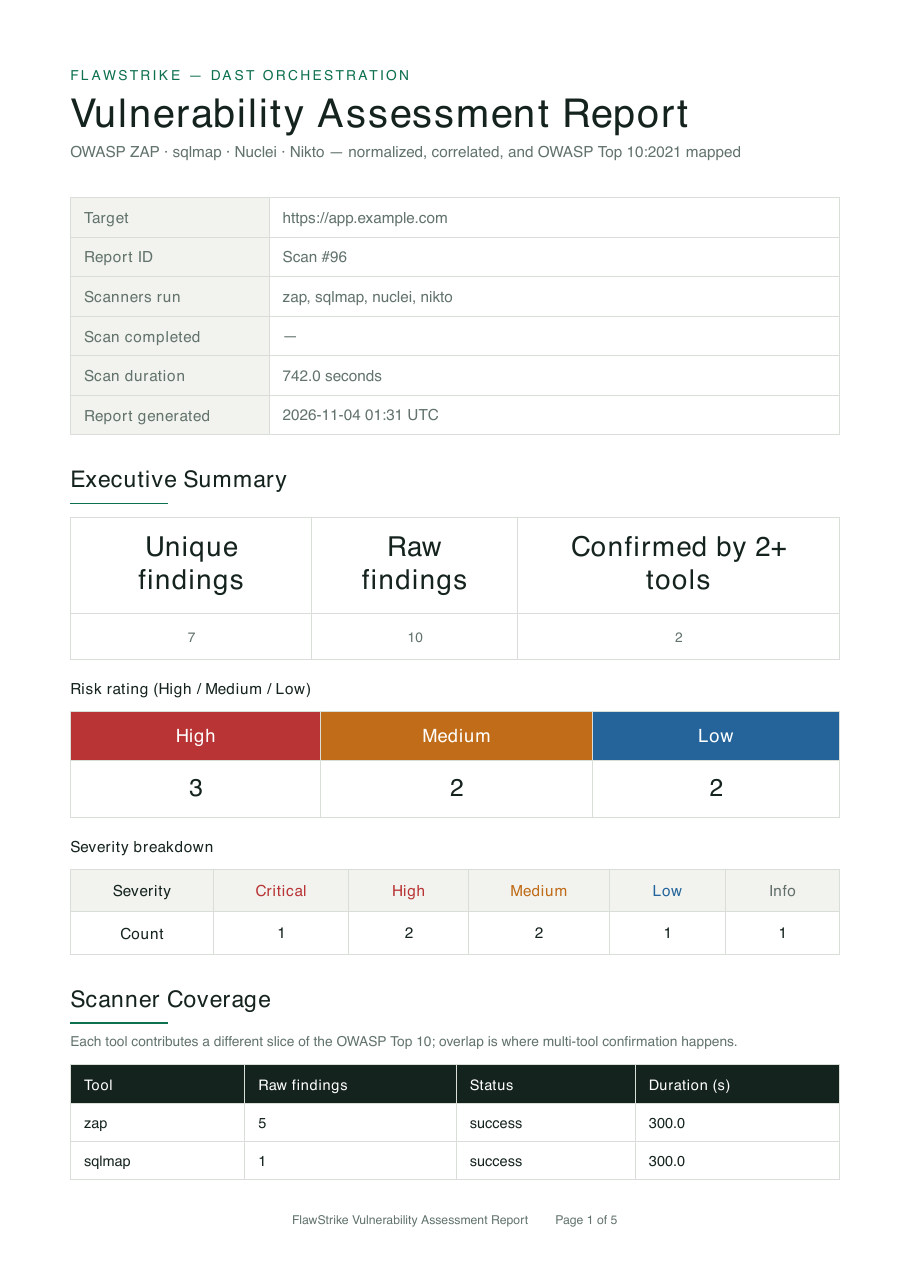
SARIF 2.1.0
Made for developer tools
SARIF is the standard format for static and security analysis results, so findings can move into tools that support it.
Download sample SARIF{
"$schema": "https://json.schemastore.org/sarif-2.1.0.json",
"version": "2.1.0",
"runs": [
{
"tool": {
...
"results": [
{
"ruleId": "A03:2021",
"level": "error",
"message": {
"text": "SQL Injection at https://app.example.com/search — parameter 'q' — reported by sqlmap, zap"
},
"locations": [
{
"physicalLocation": {
"artifactLocation": {
"uri": "https://app.example.com/search"
},
"region": {
"snippet": {
"text": "q"
}
}
}
}
],
"partialFingerprints": {
"findingId": "9c19fe1f-699d-4b4c-8785-80c23f3732c6"
},
"properties": {
"security-severity": "9.5",
...
JSON
Build on your results
Every normalized finding, ready to use in your own scripts and dashboards.
Download sample JSON{
"target": "https://app.example.com",
"total_unique_findings": 7,
"total_raw_findings": 10,
"confirmed_by_multiple_tools": 2,
"severity_summary": {
"critical": 1,
"high": 2,
"medium": 2,
"low": 1,
"info": 1
},
"findings": [
{
"tool": "sqlmap",
"vulnerability_type": "SQL Injection",
"severity": "critical",
"url": "https://app.example.com/search",
"owasp_category": "A03:2021 - Injection",
"parameter": "q",
"http_method": "GET",
"confidence": "high",
"cwe": "CWE-89",
"found_by": [
"sqlmap",
"zap"
],
"finding_id": "9c19fe1f-699d-4b4c-8785-80c23f3732c6",
"evidence": "Demo data: boolean-based blind injection in the q parameter.",
"validation_status": "needs-manual-validation"
}
]
...
Ready to test your application?
Start with 4 free scans, or ask us a question first.