Multi-engine scanning
Run OWASP ZAP, sqlmap, Nuclei and Nikto together, or choose only the engines you need for each scan.
Features
Run proven security engines from one dashboard, then turn the results into a report your team can act on.
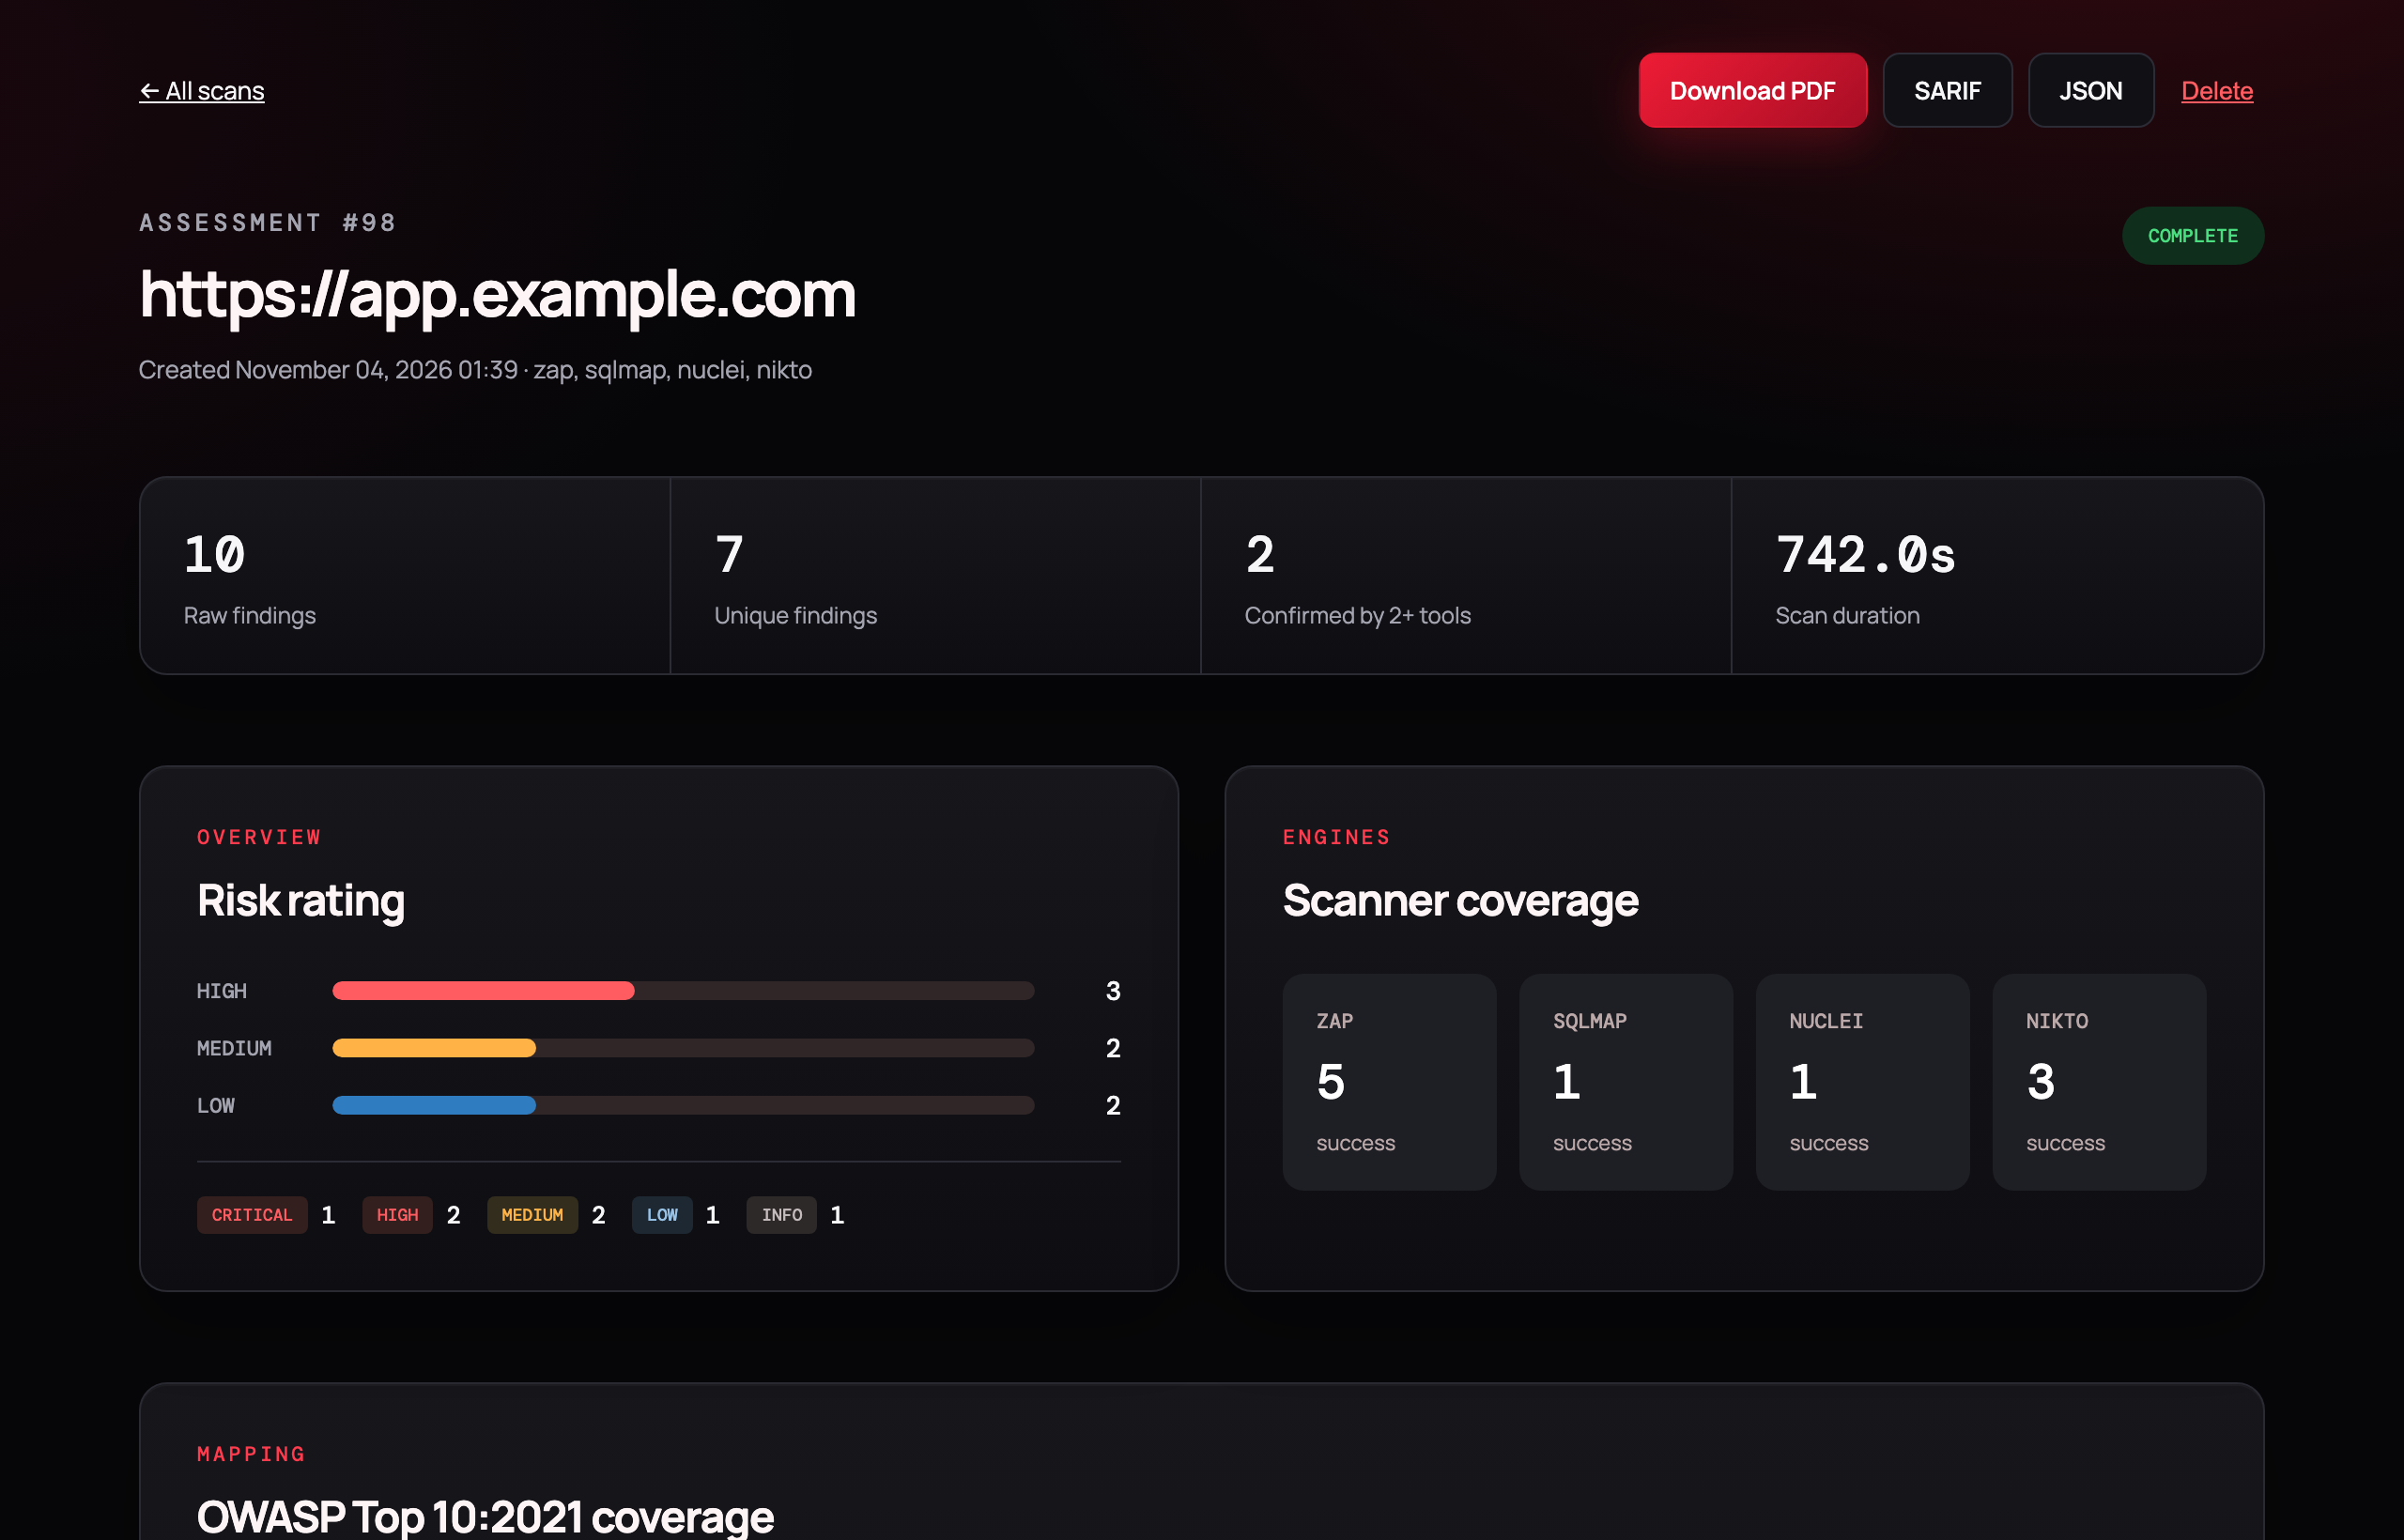
Run OWASP ZAP, sqlmap, Nuclei and Nikto together, or choose only the engines you need for each scan.
Add login details to test pages behind authentication. They're removed from the scan record once it finishes.
Compare what different user roles can reach, and catch IDOR and privilege escalation.
Duplicates are merged across engines, and findings that several engines agree on get higher confidence.
Findings are grouped by OWASP category, so you can see which risks they relate to.
Sort through results by severity and engine to decide what to fix first.
Share a report with stakeholders, or send the results to your development tools.
Start with 4 free scans, and request more from your dashboard when you need them.
Start with 4 free scans, or ask us a question first.