Access-control testing
Can your users reach what they shouldn't?
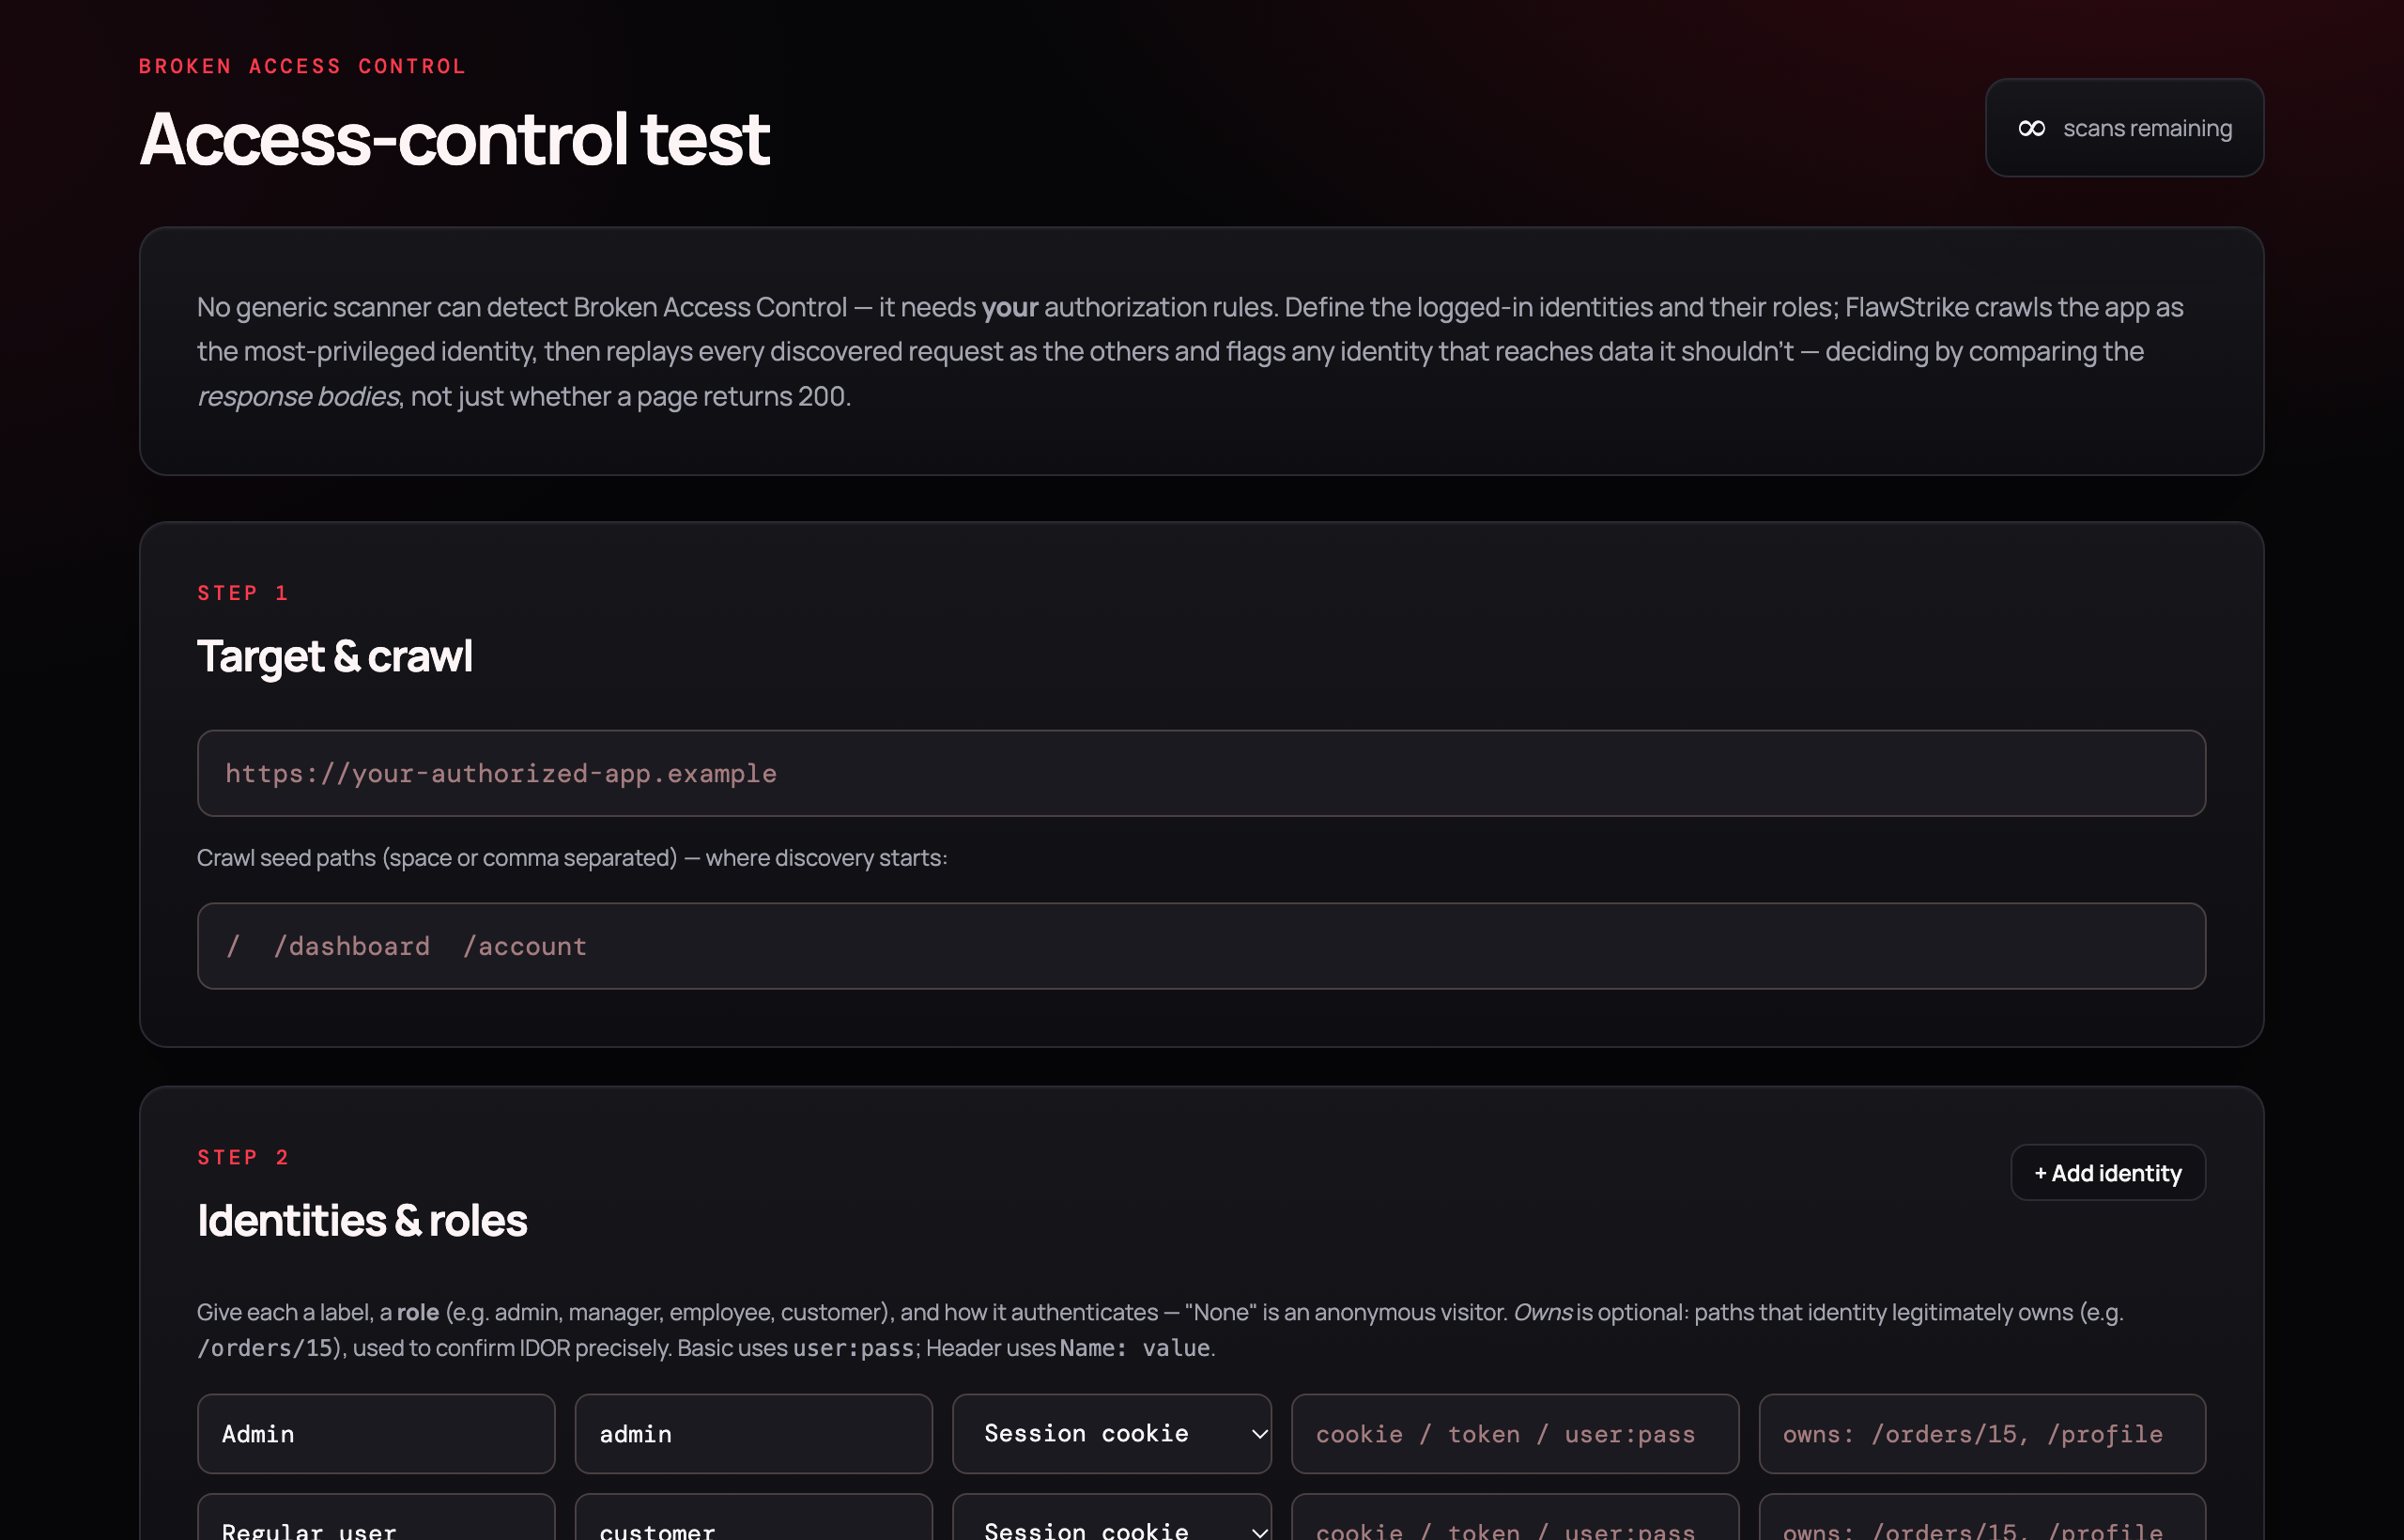
Broken access control is number one in the OWASP Top 10, and ordinary scanners rarely catch it because they don't know your rules. FlawStrike tests your app as each of your user roles.
How it works
Three steps
1Add your identities
Enter logins for the roles you want to compare, such as an admin and a regular user.
2Choose your checks
Select the kinds of access problem to test for.
3Review the results
See where one role could reach something meant for another.
Coverage
10 types of access check
Horizontal escalation / IDOR
Vertical privilege escalation
Forced browsing
Role manipulation
Direct object references in parameters
API authorization
HTTP method authorization
JWT authorization
Session authorization
Multi-tenant isolation
Ready to test your application?
Start with 4 free scans, or ask us a question first.